kernel.org
The Linux Kernel Archives
 Industry
- Computers, Electronics and Technology / Programming and Developer Software
- Origin
- United States
- Global rank
- #61,473
- Rank in United States
- #46,667
 United States
 Updated at


en
The Linux Kernel Archives
IndustryOriginGlobal rankRank in United StatesUpdated at The higher the score, the more externally observable protections the system has recorded. This page does not certify that the website is reputable, legitimate, or completely free of vulnerabilities.

As of October 16, 2026 at 06:43, kernel.org has a security score of 95.7/100 (grade A+: “Exceptional”). CyStack’s automated assessment recorded 7 issues to review after completing 100% of applicable checks. The website owner should address “DMARC blocking policy” first, then review the remaining items in order of impact.

At assessment time, CyStack did not find kernel.org or related infrastructure on any scam, phishing, or malware warning list after checking 5 online reputation sources. This result reflects external observations; it does not guarantee absolute safety or verify the organization’s legal status or reputation.
Check whether the website uses a secure connection and whether its HTTPS certificate remains valid.
Frequently asked questions
A valid SSL certificate still does not prove that kernel.org is safe, legitimate, or free of scam signals. For a more complete assessment, this report also checks phishing and malware, exposed email records, IPs and open ports, subdomains, technologies, and CVEs that may apply to observed versions.
kernel.org used a valid SSL certificate at assessment time, valid until January 12, 2027. This status may change when the certificate expires or the server configuration changes.
Review HTTPS and certificateData sources
CyStack compiles scan results from its internal cybersecurity monitoring systems, including CyStack VulnScan and CyStack Threat Intelligence, together with publicly available Internet data. The assessment only observes and analyzes information already available; it does not attempt unauthorized access, test passwords, send exploit code, or change or disrupt the assessed system.
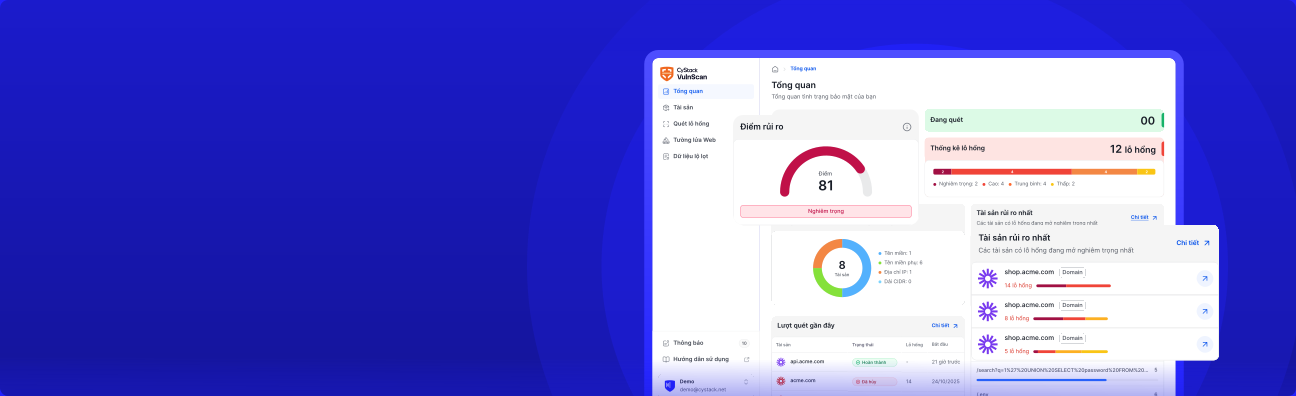
CyStack VulnScan continuously discovers assets, validates vulnerabilities, and helps security teams prioritize remediation across the enterprise.
These 3 failed checks or warnings have the greatest impact on the result for kernel.org.
Why it matters
A policy of quarantine or reject tells receiving services to move suspicious mail to spam or refuse it. A monitoring-only policy (p=none) records the problem but does not ask receivers to stop spoofed mail.
What to do
After every legitimate sender passes DMARC, move gradually to quarantine and then reject, covering 100% of messages.
Evidence and check scope
References
Identify website protection and check whether public IPs appear on warning lists.
Check domain and email settings that help prevent brand impersonation.
Remove obsolete DNS names and protect non-public systems with strong authentication, MFA, network allowlists, or a VPN.
Diagnostic information
Subdomain discovery did not complete, so the current list may be incomplete.
Evidence and check scope
Evidence and check scope
References
| SpamCop | Not listed |
| blocklist.de | Not listed |
| Spamhaus | Unavailable |
Recently completed assessments, prioritizing websites with a similar sector, country or security grade for easier comparison.