jps-stuttgart.com
シュツットガルト日本語補習授業校
共に日本を学ぶ シュツットガルト日本語補習授業校は、在ドイツの学校に通学している児童・生徒を対象とし、『学習指導要領』に示す内容を基準にして日本語で授業を提供することを主な目的として、保護者が設置・運営する学校です。
 Industry
- Science and Education / Education
- Origin
- –
- Global rank
- –
- Rank in
- –
 Updated at


en
シュツットガルト日本語補習授業校
共に日本を学ぶ シュツットガルト日本語補習授業校は、在ドイツの学校に通学している児童・生徒を対象とし、『学習指導要領』に示す内容を基準にして日本語で授業を提供することを主な目的として、保護者が設置・運営する学校です。
IndustryOriginGlobal rankRank in Updated at The higher the score, the more externally observable protections the system has recorded. This page does not certify that the website is reputable, legitimate, or completely free of vulnerabilities.

As of October 5, 2026 at 20:38, jps-stuttgart.com has a security score of 59/100 (grade F: “Low”). CyStack’s automated assessment recorded 10 issues to review after completing 98.2% of applicable checks. The website owner should address “HTTPS/TLS endpoint reachability” first, then review the remaining items in order of impact.

At assessment time, CyStack did not find jps-stuttgart.com or related infrastructure on any scam, phishing, or malware warning list after checking 5 online reputation sources. This result reflects external observations; it does not guarantee absolute safety or verify the organization’s legal status or reputation.
Addresses, servers and services that are visible from the Internet.
Frequently asked questions
A valid SSL certificate still does not prove that jps-stuttgart.com is safe, legitimate, or free of scam signals. For a more complete assessment, this report also checks phishing and malware, exposed email records, IPs and open ports, subdomains, technologies, and CVEs that may apply to observed versions.
HTTPS on jps-stuttgart.com could not be reached during this assessment, so its SSL certificate and transport encryption could not be evaluated.
Review HTTPS and certificateData sources
CyStack compiles scan results from its internal cybersecurity monitoring systems, including CyStack VulnScan and CyStack Threat Intelligence, together with publicly available Internet data. The assessment only observes and analyzes information already available; it does not attempt unauthorized access, test passwords, send exploit code, or change or disrupt the assessed system.
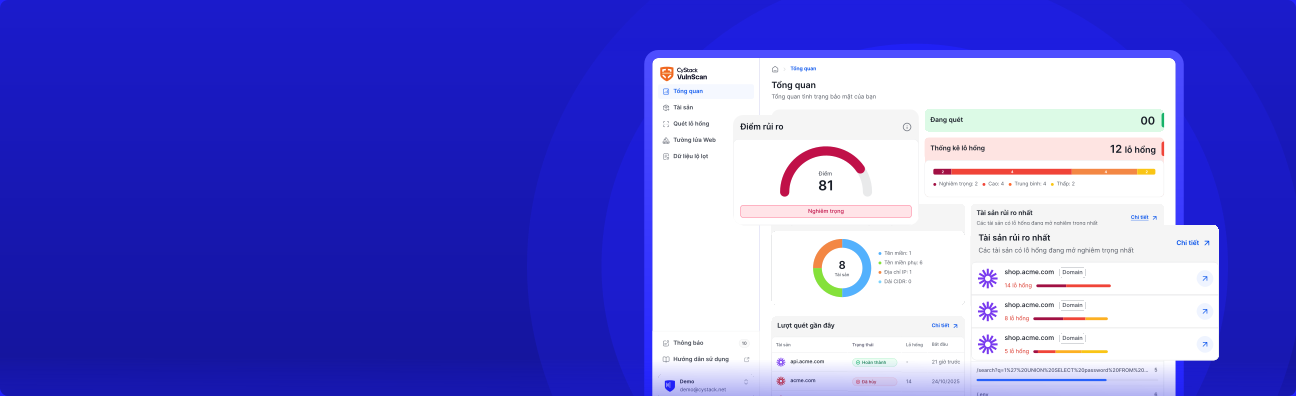
CyStack VulnScan continuously discovers assets, validates vulnerabilities, and helps security teams prioritize remediation across the enterprise.
These 3 failed checks or warnings have the greatest impact on the result for jps-stuttgart.com.
Why it matters
This check only confirms whether a TLS handshake can be established with at least one tested resolved endpoint on the HTTPS port. Certificate trust, hostname identity, validity, chain, protocol, and cryptographic strength are evaluated separately.
What to do
Provide the entire website over HTTPS using a certificate trusted by common browsers.
Diagnostic information
The scanner could not complete a TLS handshake with the HTTPS endpoint during this assessment.
Evidence and check scope
This is the port on which the scanner attempted a TLS connection. The port number alone does not prove that the port is open or that HTTPS works.
Each public IP is grouped with its open services, identified products and any CVEs that may apply to the observed version.
 216.239.32.21any-in-2015.1e100.net216.239.34.21any-in-2215.1e100.net216.239.36.21any-in-2415.1e100.net216.239.38.21any-in-2615.1e100.net
Scope of this check
This check only evaluates the homepage response and content that the scanner could reach. Other pages and sign-in flows may use different settings.
Evidence and check scope
References
Evidence and check scope
References
Product not identified
Recently completed assessments, prioritizing websites with a similar sector, country or security grade for easier comparison.