- Products & ServicesProducts & Services
- SolutionsSolutions
- PricingPricing
- CompanyCompany
- ResourcesResources

en
en
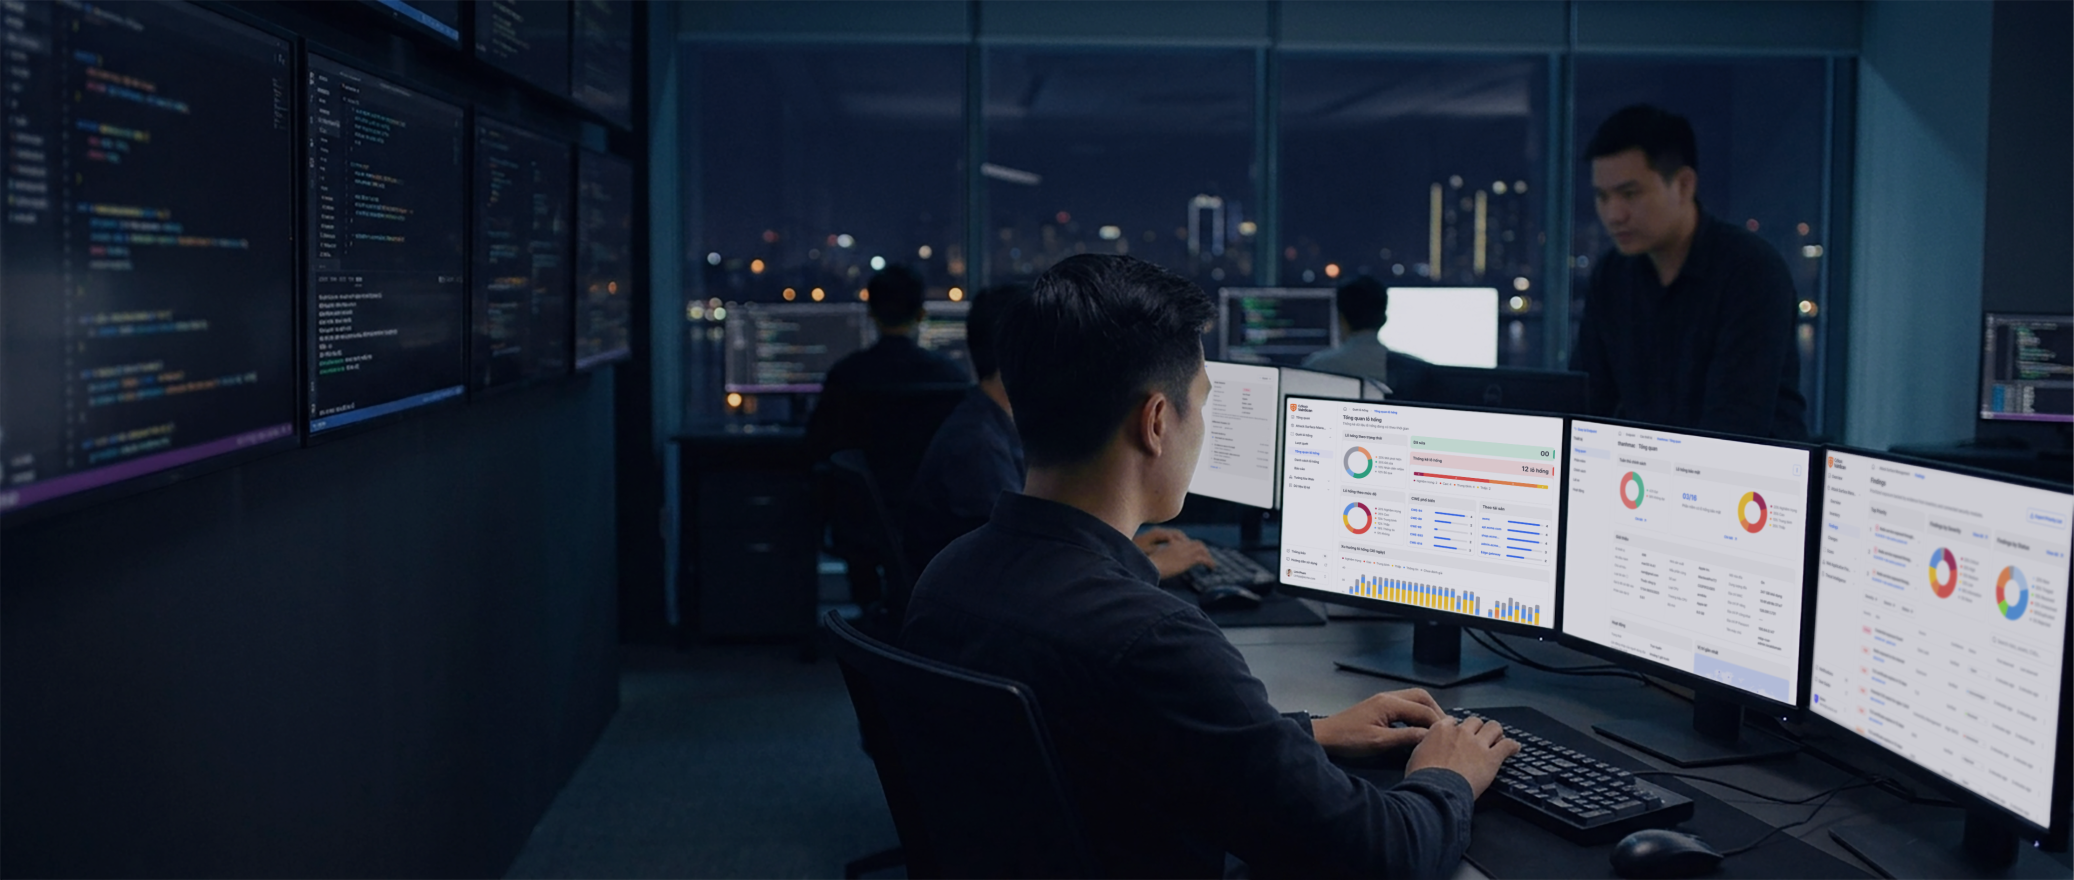
CyStack monitors your environment on your behalf, then detects and handles threats before they put your finances at risk.
A SOC (Security Operations Center) is a cybersecurity monitoring center that runs 24/7. Its analysts use SIEM, threat intelligence and automation tools to detect and stop threats before they can damage the business.
CyStack provides a managed SOC on an outsourced model: your business gets monitoring capability right away without building its own infrastructure or hiring a separate analyst team.
A single data breach costs $4.45 million on average. The brand's reputation suffers as well.
Hackers keep track of vulnerabilities in your systems and are ready to strike the moment no one is watching.
Documentation for personal data protection and tiered information system security must be ready the moment inspectors arrive.
Source: IBM
CyStack monitors your systems and responds to incidents on your behalf, so your internal team can focus on the business.
Security engineers certified in CISSP, GREM, GCIH, OSCP, CompTIA Security+ and CEH.
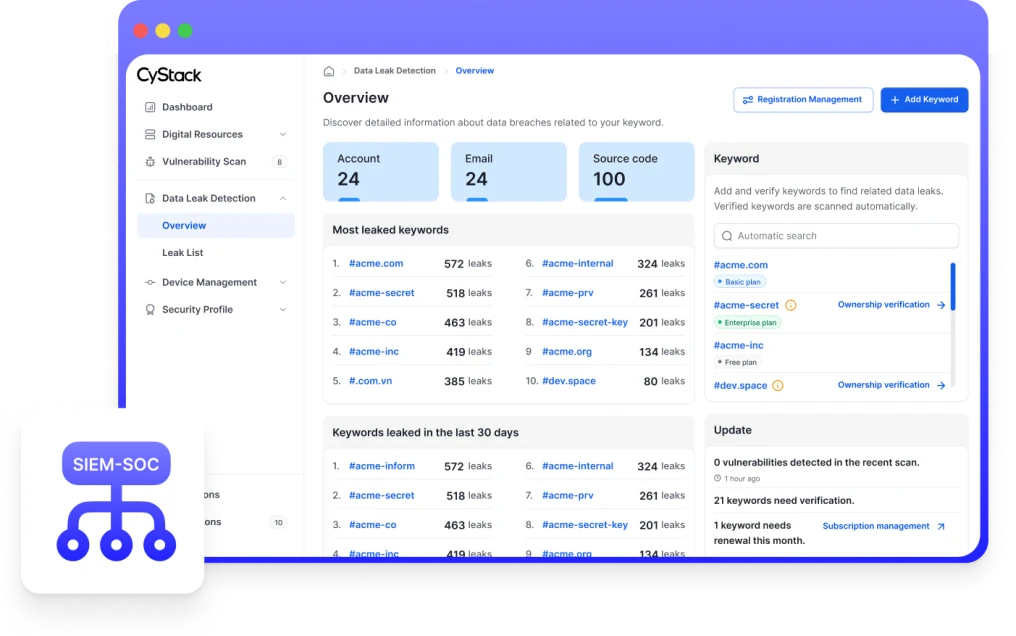
Combines a SIEM system, threat intelligence, VulnScan and tools that handle events automatically in real time.
Standard operating procedures (SOPs) and consistent response guidelines for every incident.
CyStack adjusts the scope flexibly to match the current state of each business's systems.

Servers, routers, switches and firewalls. Detects intrusions and unauthorized access.

Laptops, desktops and mobile devices. Blocks malware directly on the device.

Scans applications and software to find security vulnerabilities.

Cloud infrastructure and applications. Alerts on insecure configurations.

Databases and data stores. Detects attempts to steal data.

Helps businesses meet Decree 85, Circular 12, PCI DSS and more.

Detects and stops incidents caused by employees, contractors or partners.

We review your current state first, then build a package around your system's specifics.
95% of threats detected within 15 minutes (MTTD), with response in 30 minutes at most (MTTR).
Identifies threats early from many data sources.
Detects anomalies the moment they occur.
SIEM collects logs from servers, firewalls, endpoints and applications in one place, then correlates them to find abnormal behavior.
When logs are scattered across dozens of systems, no one can piece together the path of an attack that crosses several layers.
Review the infrastructure, applications, log sources and compliance requirements; design the monitoring architecture, alert thresholds and response SLA.
Connect the SIEM to log sources, set up detection rules, and integrate threat intelligence and alert channels.
The SOC team is on duty 24/7, analyzing logs from many sources to detect password guessing, privilege escalation or data theft.
Classify the incident and trace its source; work with your internal team to contain and remediate it, and recommend how to recover afterward.
Send weekly, monthly or quarterly reports; after each period, update detection rules and reduce noisy alerts.
CyStack's information security engineers have protected hundreds of critical infrastructure systems.
TRUSTED BY
We review the whole infrastructure and fix weak points before attackers exploit them.
Periodic reports that meet legal requirements and industry standards.
Talk easily with hands-on engineers, with no intermediary or third party in between.
Reduce MTTR and detect targeted attacks (APT) early.
The companies below have acknowledged the CyStack team for discovering and responsibly disclosing critical vulnerabilities in their products.
CyStack experts have presented security research at the international conferences below.
Our experts are ready to give in-depth advice on whether your business is ready for a SOC service, where to set your goals and what a reasonable scope looks like.