ignica.com
Scan&Go ignicaのご紹介
ignica (イグニカ) は、これからのリテールの在り方の 創造を目指して U.S.M.Hから誕生しました。拡張性の高いプラットフォームで、必要に応じた機能の 追加・連携を可能にします。
 Industry
- Food and Drink
- Origin
- Japan
- Global rank
- #294,433
- Rank in Japan
- #17,226
 Japan
 Updated at


en
Scan&Go ignicaのご紹介
ignica (イグニカ) は、これからのリテールの在り方の 創造を目指して U.S.M.Hから誕生しました。拡張性の高いプラットフォームで、必要に応じた機能の 追加・連携を可能にします。
IndustryOriginGlobal rankRank in JapanUpdated at The higher the score, the more externally observable protections the system has recorded. This page does not certify that the website is reputable, legitimate, or completely free of vulnerabilities.

As of October 23, 2026 at 19:21, ignica.com has a security score of 81.1/100 (grade B: “Good”). CyStack’s automated assessment recorded 13 issues to review after completing 100% of applicable checks. The website owner should address “Known-exploited CVE candidates” first, then review the remaining items in order of impact.

At assessment time, CyStack did not find ignica.com or related infrastructure on any scam, phishing, or malware warning list after checking 5 online reputation sources. This result reflects external observations; it does not guarantee absolute safety or verify the organization’s legal status or reputation.
Check whether the website uses a secure connection and whether its HTTPS certificate remains valid.
Frequently asked questions
A valid SSL certificate still does not prove that ignica.com is safe, legitimate, or free of scam signals. For a more complete assessment, this report also checks phishing and malware, exposed email records, IPs and open ports, subdomains, technologies, and CVEs that may apply to observed versions.
ignica.com used a valid SSL certificate at assessment time, valid until December 21, 2026. This status may change when the certificate expires or the server configuration changes.
Review HTTPS and certificateData sources
CyStack compiles scan results from its internal cybersecurity monitoring systems, including CyStack VulnScan and CyStack Threat Intelligence, together with publicly available Internet data. The assessment only observes and analyzes information already available; it does not attempt unauthorized access, test passwords, send exploit code, or change or disrupt the assessed system.
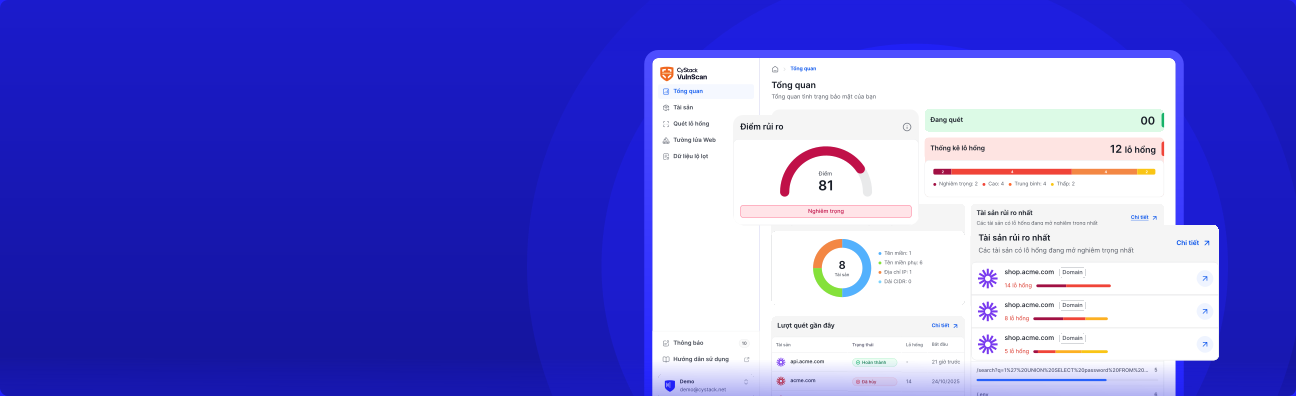
CyStack VulnScan continuously discovers assets, validates vulnerabilities, and helps security teams prioritize remediation across the enterprise.
These 3 failed checks or warnings have the greatest impact on the result for ignica.com.
Why it matters
This check asks whether an applicable CVE candidate also appears in the CISA Known Exploited Vulnerabilities (KEV) catalog. A positive match means attackers have used that vulnerability in real incidents and warrants urgent investigation, but the installed software still needs to be confirmed as affected.
What to do
Verify the installed product immediately and follow the CISA and vendor instructions for mitigation, patching, or upgrading if it is affected.
Evidence and check scope
Identify website protection and check whether public IPs appear on warning lists.
Check domain and email settings that help prevent brand impersonation.
16 additional evidence fields are not shown here.
Scope of this check
This check only evaluates the homepage response and content that the scanner could reach. Other pages and sign-in flows may use different settings.
Evidence and check scope
References
Confirm the exact installed package and read the vendor advisory. If that installation is affected, apply the vendor patch or upgrade to a fixed version.
Evidence and check scope
16 additional evidence fields are not shown here.
References
| SpamCop | Not listed |
| blocklist.de | Not listed |
| Spamhaus | Unavailable |
Recently completed assessments, prioritizing websites with a similar sector, country or security grade for easier comparison.