Tư Vấn, Triển Khai Chuyển đổi Số Toàn Diện Cho Doanh Nghiệp
iERP là đơn vị tư vấn, triển khai chuyển đổi số toàn diện cho DN như:ERP, BI, Big Data, ECM, e-Invoice. Đối tác của Oracle, Tableau, Microsoft
Industry
Computers, Electronics and Technology
Origin
Vietnam
Global rank
#3,529,964
Rank in Vietnam
#50,269
Updated at
C79/100
Security level
Fair
Data confidence
High
Scope checked
97.3%
The higher the score, the more externally observable protections the system has recorded. This page does not certify that the website is reputable, legitimate, or completely free of vulnerabilities.
Is the website “ierp.vn” safe?
As of October 24, 2026 at 11:19, ierp.vn has a security score of 79/100 (grade C: “Fair”). CyStack’s automated assessment recorded 13 issues to review after completing 97.3% of applicable checks. The website owner should address “Known-exploited CVE candidates” first, then review the remaining items in order of impact.
Does ierp.vn show known scam, phishing, or malware signals?
At assessment time, CyStack did not find ierp.vn or related infrastructure on any scam, phishing, or malware warning list after checking 5 online reputation sources. This result reflects external observations; it does not guarantee absolute safety or verify the organization’s legal status or reputation.
A valid SSL certificate still does not prove that ierp.vn is safe, legitimate, or free of scam signals. For a more complete assessment, this report also checks phishing and malware, exposed email records, IPs and open ports, subdomains, technologies, and CVEs that may apply to observed versions.
Does ierp.vn use HTTPS, and is its SSL certificate valid?
ierp.vn used a valid SSL certificate at assessment time, valid until January 9, 2027. This status may change when the certificate expires or the server configuration changes.
Data compiled from CyStack cybersecurity monitoring systems
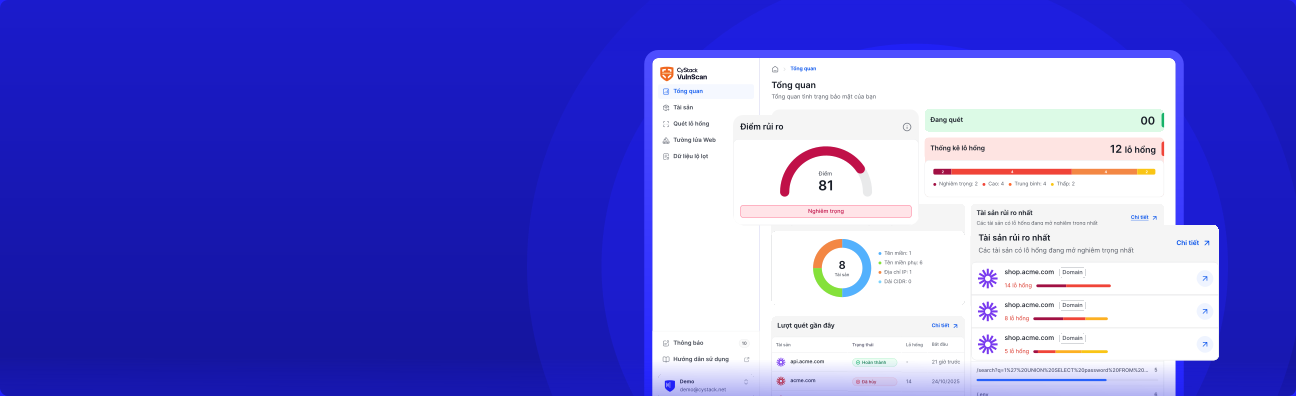
CyStack compiles scan results from its internal cybersecurity monitoring systems, including CyStack VulnScan and CyStack Threat Intelligence, together with publicly available Internet data. The assessment only observes and analyzes information already available; it does not attempt unauthorized access, test passwords, send exploit code, or change or disrupt the assessed system.
These 3 failed checks or warnings have the greatest impact on the result for ierp.vn.
Known-exploited CVE candidatesFound 1 known-exploited candidate(s), but the external product fingerprint requires verification.Critical
Why it matters
This check asks whether an applicable CVE candidate also appears in the CISA Known Exploited Vulnerabilities (KEV) catalog. A positive match means attackers have used that vulnerability in real incidents and warrants urgent investigation, but the installed software still needs to be confirmed as affected.
What to do
Verify the installed product immediately and follow the CISA and vendor instructions for mitigation, patching, or upgrading if it is affected.
Public management service exposureA confirmed public management service was found: 150.95.16.71:9090 (ssh).High
Why it matters
Remote administration services such as RDP, VNC, Docker, Kubernetes, and management consoles are high-value targets. Public exposure allows anyone on the Internet to attempt passwords or exploit an unpatched service.
What to do
Remove direct Internet access and require a VPN, a hardened access gateway, or trusted source networks; also use MFA where supported.
Allowed browser content (CSP)The inspected root HTML response does not include a Content-Security-Policy header.High
Why it matters
Content Security Policy (CSP) limits where scripts, styles, frames, and other browser content may come from. A strong policy reduces the impact if an attacker manages to inject content into a page.
What to do
Define only the sources the application needs, test the policy before activating it, and avoid broad wildcard (*) rules, unsafe-inline, and unsafe-eval where possible.
–
Operating system
Public infrastructure and exposed software
Each public IP is grouped with its open services, identified products and any CVEs that may apply to the observed version.
Completed testing of 58 TCP ports
150.95.16.71cnode001.secureweb.vn
3 open services16 identified products
Hosting or network providerProvider not identified
Network location–
ASN–
80HTTPNginx
ProductVersionPotential vulnerabilities
Nginx
Other website-level technologiesThese products were observed from the public website, but the available evidence was not sufficient to assign them safely to one IP and port.
e-business suiteVersion not visibleVersion not visible
ConfidenceMedium
Have @ierp.vn email addresses appeared in exposed data or information-stealer (infostealer) logs?
There are currently 3 exposed email records matching the ierp.vn domain. These records may be old or already resolved. The website owner should verify them before resetting passwords or locking related accounts.
Which public IPs, services, and ports does ierp.vn expose?
The assessment observed 1 public IPs and 3 open ports for ierp.vn. An open port is not the same as a vulnerability, but the website owner should keep every public service updated and appropriately restrict access.
How many subdomains of ierp.vn have been discovered?
The assessment observed 9 public subdomains of ierp.vn. This list can reveal additional entry points such as APIs, administration systems, or test environments, but it does not mean that every subdomain is risky.
The PKCS#11 feature in ssh-agent in OpenSSH before 9.3p2 has an insufficiently trustworthy search path, leading to remote code execution if an agent is forwarded to an attacker-controlled system. (Code in /usr/lib is not necessarily safe for loading into ssh-agent.) NOTE: this issue exists because of an incomplete fix for CVE-2016-10009.
WordPress is a free and open-source content management system written in PHP and paired with a MySQL or MariaDB database. Features include a plugin architecture and a template system.
Matched product: WordPress 7.0.2 Confidence: Medium
An unauthenticated attacker can make `get_page_template()` page-template resolution include a chosen readable local `.php` file outside the active theme directories. If relevant pre-conditions for both the server and the active theme are met, this can lead to RCE.
Contact Form 7 is an WordPress plugin which can manage multiple contact forms. The form supports Ajax-powered submitting, CAPTCHA, Akismet spam filtering.
jQuery is a JavaScript library which is a free, open-source software designed to simplify HTML DOM tree traversal and manipulation, as well as event handling, CSS animation, and Ajax.
ssh in OpenSSH before 10.4 can have a use-after-free when a server changes its host key during a key re-exchange. (This outcome occurs only on the client side.)
In OpenSSH before 10.3, a file downloaded by scp may be installed setuid or setgid, an outcome contrary to some users' expectations, if the download is performed as root with -O (legacy scp protocol) and without -p (preserve mode).
OpenSSH before 10.3 mishandles the authorized_keys principals option in uncommon scenarios involving a principals list in conjunction with a Certificate Authority that makes certain use of comma characters.
sshd in OpenSSH before 10.4 allows remote attackers to cause a denial of service (resource consumption from excessive authentication attempts) because MaxAuthTries was mishandled for GSSAPIAuthentication.
scp in OpenSSH through 8.3p1 allows command injection in the scp.c toremote function, as demonstrated by backtick characters in the destination argument. NOTE: the vendor reportedly has stated that they intentionally omit validation of "anomalous argument transfers" because that could "stand a great chance of breaking existing workflows."
sshd in OpenSSH 6.2 through 8.x before 8.8, when certain non-default configurations are used, allows privilege escalation because supplemental groups are not initialized as expected. Helper programs for AuthorizedKeysCommand and AuthorizedPrincipalsCommand may run with privileges associated with group memberships of the sshd process, if the configuration specifies running the command as a different user.
An issue was discovered in OpenSSH 7.9. Due to missing character encoding in the progress display, a malicious server (or Man-in-The-Middle attacker) can employ crafted object names to manipulate the client output, e.g., by using ANSI control codes to hide additional files being transferred. This affects refresh_progress_meter() in progressmeter.c.
In OpenSSH 7.9, due to accepting and displaying arbitrary stderr output from the server, a malicious server (or Man-in-The-Middle attacker) can manipulate the client output, for example to use ANSI control codes to hide additional files being transferred.
A vulnerability was found in OpenSSH when the VerifyHostKeyDNS option is enabled. A machine-in-the-middle attack can be performed by a malicious machine impersonating a legit server. This issue occurs due to how OpenSSH mishandles error codes in specific conditions when verifying the host key. For an attack to be considered successful, the attacker needs to manage to exhaust the client's memory resource first, turning the attack complexity high.
In ssh in OpenSSH before 9.6, OS command injection might occur if a user name or host name has shell metacharacters, and this name is referenced by an expansion token in certain situations. For example, an untrusted Git repository can have a submodule with shell metacharacters in a user name or host name.
In sftp in OpenSSH before 10.6, a server can trigger directory traversal (causing files to be written to unintended locations) during a recursive copy operation.
In sshd and ssh in OpenSSH before 10.6, there is no check for whether the maximum packet length is exceeded during decompression of highly compressed data.
OpenSSH before 10.3 can use unintended ECDSA algorithms. Listing of any ECDSA algorithm in PubkeyAcceptedAlgorithms or HostbasedAcceptedAlgorithms is misinterpreted to mean all ECDSA algorithms.
sshd in OpenSSH before 10.4 has an undocumented security-relevant behavior: GSSAPIStrictAcceptorCheck has no value if the server is in Windows Active Directory.
An issue was discovered in OpenSSH 7.9. Due to the scp implementation being derived from 1983 rcp, the server chooses which files/directories are sent to the client. However, the scp client only performs cursory validation of the object name returned (only directory traversal attacks are prevented). A malicious scp server (or Man-in-The-Middle attacker) can overwrite arbitrary files in the scp client target directory. If recursive operation (-r) is performed, the server can manipulate subdirectories as well (for example, to overwrite the .ssh/authorized_keys file).
The client side in OpenSSH 5.7 through 8.4 has an Observable Discrepancy leading to an information leak in the algorithm negotiation. This allows man-in-the-middle attackers to target initial connection attempts (where no host key for the server has been cached by the client). NOTE: some reports state that 8.5 and 8.6 are also affected.
The SSH transport protocol with certain OpenSSH extensions, found in OpenSSH before 9.6 and other products, allows remote attackers to bypass integrity checks such that some packets are omitted (from the extension negotiation message), and a client and server may consequently end up with a connection for which some security features have been downgraded or disabled, aka a Terrapin attack. This occurs because the SSH Binary Packet Protocol (BPP), implemented by these extensions, mishandles the handshake phase and mishandles use of sequence numbers. For example, there is an effective attack against SSH's use of ChaCha20-Poly1305 (and CBC with Encrypt-then-MAC). The bypass occurs in chacha20-poly1305@openssh.com and (if CBC is used) the -etm@openssh.com MAC algorithms. This also affects Maverick Synergy Java SSH API before 3.1.0-SNAPSHOT, Dropbear through 2022.83, Ssh before 5.1.1 in Erlang/OTP, PuTTY before 0.80, AsyncSSH before 2.14.2, golang.org/x/crypto before 0.17.0, libssh before 0.10.6, libssh2 through 1.11.0, Thorn Tech SFTP Gateway before 3.4.6, Tera Term before 5.1, Paramiko before 3.4.0, jsch before 0.2.15, SFTPGo before 2.5.6, Netgate pfSense Plus through 23.09.1, Netgate pfSense CE through 2.7.2, HPN-SSH through 18.2.0, ProFTPD before 1.3.8b (and before 1.3.9rc2), ORYX CycloneSSH before 2.3.4, NetSarang XShell 7 before Build 0144, CrushFTP before 10.6.0, ConnectBot SSH library before 2.2.22, Apache MINA sshd through 2.11.0, sshj through 0.37.0, TinySSH through 20230101, trilead-ssh2 6401, LANCOM LCOS and LANconfig, FileZilla before 3.66.4, Nova before 11.8, PKIX-SSH before 14.4, SecureCRT before 9.4.3, Transmit5 before 5.10.4, Win32-OpenSSH before 9.5.0.0p1-Beta, WinSCP before 6.2.2, Bitvise SSH Server before 9.32, Bitvise SSH Client before 9.33, KiTTY through 0.76.1.13, the net-ssh gem 7.2.0 for Ruby, the mscdex ssh2 module before 1.15.0 for Node.js, the thrussh library before 0.35.1 for Rust, and the Russh crate before 0.40.2 for Rust.
sftp in OpenSSH before 10.4 does not properly constrain the location of downloaded files when "sftp server:/path ." is used with an attacker-controlled server.


 Industry
 Vietnam
 Updated at