CWE-280: Improper Handling of Insufficient Permissions or Privileges

CWE-280 là gì?

CWE-280 là Improper Handling of Insufficient Permissions or Privileges. Lỗi phát sinh khi the product does not handle or incorrectly handles when it has insufficient privileges to access resources or functionality as specified by their permissions. Hiện có 36 lỗ hổng trong kho dữ liệu liên quan đến CWE-280 và không có lỗ hổng nào nằm trong danh mục khai thác thực tế của CISA.

Đang phân tích dữ liệu...
THỨ HẠNG OWASP TOP 10:202510 — A10:2025 — Mishandling of Exceptional Conditions
Tổng số CVE liên quan (365 ngày)36
Mức trừu tượngCơ bản
Khả năng khai thác-

Số lượng lỗ hổng nằm trong CWE-280

36 lỗ hổngTăng 227% so với cùng kỳ

Không có dữ liệu

Chưa có dữ liệu về lỗ hổng trong CISA KEV cho CWE-280

Định nghĩa chính thức

TheoMitre CWE

Đặc điểm

Dữ liệu MITRE CWE chính thức

Giai đoạn hình thành

  • Hiện thực hóa: REALIZATION: This weakness is caused during implementation of an architectural security tactic.

Hậu quả thường gặp

Dữ liệu MITRE CWE chính thức
Tác độngPhạm viDiễn giải
Khác, Thay đổi logic thực thiKhác-

Biện pháp giảm thiểu rủi ro

Dữ liệu MITRE CWE chính thức
  1. Phân tách đặc quyền · Kiến trúc và thiết kếCompartmentalize the system to have "safe" areas where trust boundaries can be unambiguously drawn. Do not allow sensitive data to go outside of the trust boundary and always be careful when interfacing with a compartment outside of the safe area. Ensure that appropriate compartmentalization is built into the system design, and the compartmentalization allows for and reinforces privilege separation functionality. Architects and designers should rely on the principle of least privilege to decide the appropriate time to use privileges and the time to drop privileges.
  2. Hiện thực hóaAlways check to see if you have successfully accessed a resource or system functionality, and use proper error handling if it is unsuccessful. Do this even when you are operating in a highly privileged mode, because errors or environmental conditions might still cause a failure. For example, environments with highly granular permissions/privilege models, such as Windows or Linux capabilities, can cause unexpected failures.

Cách phát hiện trong hệ thống

Dữ liệu MITRE CWE chính thức
Phương phápCách làmHiệu quả
Phân tích tĩnh tự độngAutomated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)-

Lỗ hổng điển hình

Nguồn (2)

CWE™ Program, operated by The MITRE Corporation. Copyright © 2006–2026, The MITRE Corporation. The MITRE Corporation hereby grants you a non-exclusive, royalty-free license to use CWE for research, development, and commercial purposes. CWE Terms of Use.

Tìm hiểu thêm

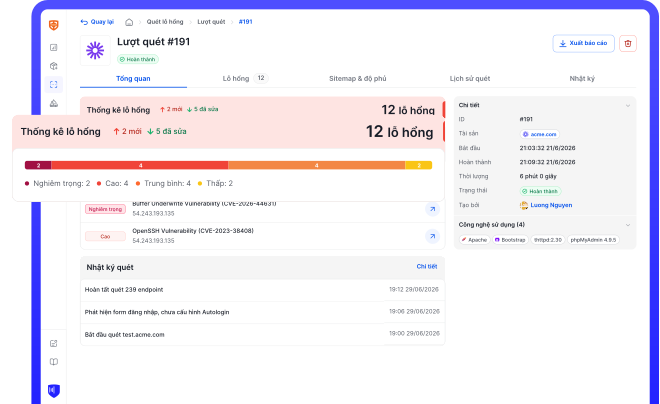
Kiểm tra chuyên sâu cùng giải pháp quản lý rủi ro Web toàn diện

Giải pháp CyStack VulnScan liên tục phát hiện tài sản, xác minh lỗ hổng và giúp đội ngũ bảo mật ưu tiên khắc phục cho toàn bộ doanh nghiệp.